
Max Yakub
∙
Passwordless Privileged Access Management (PAM): A Practical Guide
Max Yakub
∙
Passwordless Privileged Access Management (PAM): A Practical Guide
Max Yakub
∙
Passwordless Privileged Access Management (PAM): A Practical Guide
Passwordless privileged access management (PAM) removes passwords and one-time codes from admin logins and replaces them with phishing-resistant authentication, plus just-in-time role activation instead of standing access. It matters because credential theft remains the most common way attackers get into a network, and privileged accounts are the ones worth stealing.
This guide covers what privileged access management is, why passwordless authentication changes its risk profile, the core capabilities a modern PAM program needs, and a rollout plan you can actually execute.
What is privileged access management?
Privileged access management is the set of policies and tools that control how highly empowered identities, human admins, third-party operators, service accounts, and machine identities get, use, and give up elevated rights.
A PAM program governs:
Issuing and recording privileged sessions
Secret vaulting and rotation
Step-up authentication at moments of risk
Approvals and time-bound access
Monitoring and forensic audit trails
NIST and CISA now treat PAM as a core pillar of Zero Trust. Under that model, privileged access is never implicit. It's evaluated per request and verified continuously, not granted once and left standing.
Who counts as a privileged identity?
Privileged identities go well beyond domain admins. They include:
Humans: cloud and infrastructure admins, DBAs, SOC responders, SREs with emergency access, third-party maintainers
Machines: service accounts, workload identities (containers, serverless), CI/CD automation bots, embedded API keys
Non-human identities are often the most dangerous. They tend to be over-provisioned, long-lived, and shared across teams, which makes them attractive to attackers and hard to audit. NIST SP 800-53's AC-2 controls call for formal account management and dynamic activation specifically because unmanaged accounts accumulate into standing privilege, and standing privilege is what turns into an attacker's first foothold.
Why credential theft drives PAM strategy
The 2025 Verizon DBIR found credential abuse is still the most common initial access vector into breached networks, and ransomware was present in 44% of all breaches reviewed, up from 32% the year before.
Every long-lived password, token, or static key is a liability. Every privileged session is a potential launch point for lateral movement. The job of PAM is to shrink that exposure window and require stronger, device-bound proof of identity before granting access.
Why go passwordless for privileged access
Passwordless authentication matters most exactly where the stakes are highest: admin portals, hypervisor consoles, cloud control planes, break-glass entry points, and remote shells.
Phishing is still the dominant way human credentials get stolen. Phishing-resistant multi-factor methods, WebAuthn/FIDO2 or PKI-backed smart cards (PIV/CAC), remove reusable codes entirely and bind the credential to the origin being accessed. That stops credential replay on look-alike sites and closes off push-fatigue and SIM-swap attacks that still work against legacy MFA.
OMB's federal Zero Trust strategy requires agencies to offer phishing-resistant authentication. CISA's guidance narrows that to two accepted patterns: FIDO-based and PKI-based authenticators. For PAM, that means admin sign-in should never depend on a password or a one-time code, especially for high-impact roles.
The problem with vaulted and shared passwords
Traditional PAM vaults reduce password sprawl, but they don't eliminate password risk. Any credential a human can check out can be phished, shoulder-surfed, keylogged, or reused. Pass-the-hash and token replay attacks bypass knowledge of the secret entirely.
A passwordless-first design removes this attack class by refusing to issue passwords to people at all. Humans get origin-bound authenticators; machines get brokered, ephemeral credentials.
Phishing-resistant MFA for admins
WebAuthn binds a private key inside a secure authenticator to a specific origin. The browser won't present that key to a fraudulent site. PKI smart cards achieve the same guarantee through certificate-based mutual TLS or signed assertions.
Both require user presence or verification, pairing something the user has with something the user is. For PAM, require phishing-resistant factors at every role activation or elevation event, not just at initial login.
Ephemeral credentials and just-in-time elevation
Standing privilege is attacker oxygen. PAM should issue rights just-in-time, for a narrow window, and revoke them automatically.
Microsoft Entra PIM is a common example for cloud roles: time- and approval-based activation instead of always-on access. For non-human identities, replace static long-lived credentials with:
Short-duration SSH certificates
Database credentials generated on demand
Cloud role credentials issued via federation instead of stored keys
If a token leaks, it expires fast. If a session goes rogue, revocation is immediate and attributable to a specific event.
Zero Trust principles applied to PAM
Zero Trust places a policy decision point and a policy enforcement point in front of every access request, fed by signals about identity, device, workload, and context.
Applied to PAM, that means privilege elevation isn't a one-time grant. It's conditional and continuously re-evaluated. NIST SP 800-207 sets the pattern: no implicit trust from network location, explicit authorization per resource, continuous monitoring.
Continuous verification and least privilege
Least privilege is a moving target. The right permission at 2:03pm may be wrong at 2:15pm.
Continuous verification uses device posture, geovelocity, workload integrity, and anomaly signals to decide whether a privileged session should continue, be constrained, or be forced to re-authenticate. CISA's Zero Trust Maturity Model v2.0 frames this as a progression from basic login gates to adaptive, risk-informed enforcement.
Policy decision and enforcement points
Model privileged flows with an explicit policy decision point (the policy engine) and policy enforcement point (the broker or connector) in front of every console and protocol.
The enforcement point terminates admin connections, injects credentials, records sessions, enforces command controls, and can cut a session on policy violation. The decision point evaluates identity strength, device health, behavior, resource sensitivity, and ticket linkage before allowing or altering access. This pattern applies whether you're brokering RDP/SSH or approving a cloud role activation.
Segmented admin workstations
Admin activity should originate only from hardened, segmented Privileged Access Workstations (PAWs), never from daily-use endpoints exposed to email and the open web.
Pair PAWs with device-trust checks at the moment of elevation. Don't allow role activation from an unmanaged or non-compliant device, even with perfect credentials.
Core PAM capabilities and where passwordless fits
Capability | What it does | Where passwordless changes it |
|---|---|---|
Credential vaulting and rotation | Stores and rotates secrets for break-glass and legacy systems | Becomes the exception, not the default; short-lived brokered credentials replace human-visible passwords |
Session management | Brokers, records, and controls privileged sessions | Pairs with passwordless admin login and JIT elevation for full forensic coverage |
Approval workflows | Time-boxes access and gates destructive changes | Calibrates friction to risk instead of applying blanket delays |
Secrets management for CI/CD | Issues runtime credentials to apps and pipelines | Short-lived tokens replace embedded static secrets |
Rollout plan
A PAM rollout wins by hardening the systems that would hurt most if abused, not by trying to cover everything at once.
Step 1: Prioritize crown jewels and remote access first.
Front-load two categories: crown-jewel systems (cloud control planes, directory services, hypervisors, CI/CD orchestrators, KMS/HSM consoles, production databases, identity providers, monitoring platforms with write access) and remote access (VPNs, bastion hosts, web admin portals, any management plane exposed to the internet). Commit early to phishing-resistant authentication and just-in-time elevation on both tracks. Defer everything else until those flows are solid.
Step 2: Find the shortcuts.
Prioritization is a living map, not a static spreadsheet. Expect to find shortcut tooling: old consoles kept alive for break/fix, direct RDP/SSH that bypasses the broker, legacy dashboards with super-user cookies. Pull these into scope early so every privileged entry point routes through the same policy engine.
Step 3: Build the admin inventory.
Enumerate every privileged identity and pathway: human roles (cloud, directory, database, SOC, SRE on-call), machines (daemons, scheduled jobs), workloads (containers, serverless), and service accounts. Map each to the consoles, protocols, and APIs they use, and the approvals currently required. Expect to find shadow admins, dormant but dangerous rights inherited through nested groups or old projects.
Step 4: Design the policy model.
Separate "who may ever become privileged" from "who is privileged right now." That's the core of just-in-time access: permissions stay potential until activated by strong authentication, ticket linkage, approval, and context checks.
Step 5: Run a two-stage pilot.
Stage one proves the login ceremony for admin consoles and brokers RDP/SSH sessions through a policy enforcement point that records and enforces policy; confirm device posture checks work and non-compliant endpoints get blocked. Stage two adds approvals and time-boxes, then removes legacy access paths and passwords for the pilot cohort. Exit criteria: no privileged web console accepts passwords or one-time codes for pilot users, all shell access routes through the broker, every elevation requires phishing-resistant step-up and expires, and break-glass is configured and tested.
Step 6: Phase out passwords.
Deprecating passwords is a phased outcome, not a single switch. For each privileged system, track when passwords were last used, by whom, and for what. Where legacy systems force a vault, make sure humans never see the password, use brokered injection or ephemeral certificates, and rotate after every automated use.
Monitoring, audit, and KPIs
A rollout isn't finished until you can prove it works and catch drift before it matters.
What to log: identity, assurance level, and authenticator type; device posture, source IP, and geolocation; policy decisions (allow, deny, step-up required); approvals and justifications; session start/stop, target system, commands, file transfer attempts, and termination reason.
KPIs worth tracking: privileged session count and median duration by system and role; elevation rate and time to approval; emergency access usage and time since last break-glass test; drift between source-of-truth entitlements and actual observed privileges; and password exposure, meaning how many privileged systems still accept passwords or OTP for admins, trending to zero.
Common pitfalls
Leaving recovery flows phishable.
If break-glass or account recovery hinges on email links, SMS codes, or voice calls, an attacker only needs to steer you into that lane to bypass every strong control you built elsewhere. Recovery deserves the same rigor as daily admin login: hardware-backed authenticators, out-of-band checks, minimal exempted accounts, and immediate review after every use.
Shadow admins and unmanaged service accounts.
These accumulate through nested groups, legacy migrations, and one-off exceptions. Run a standing discover-and-remediate loop: flag identities with elevated rights unused in 90 days, accounts without owners, and credentials that never rotate.
Where usernameless and passwordless authentication fits
Origin-bound, hardware-backed authentication is table stakes for privileged accounts. WebAuthn/FIDO2 covers web-based admin consoles. PIV/CAC smart cards remain standard in regulated sectors that require certificate-based authentication.
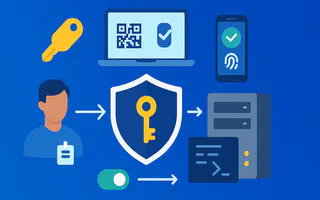
WWPass takes this further for administrators specifically: usernameless and passwordless sign-in with phishing-resistant authenticators and device binding, built on a distributed zero-trust architecture rather than a single stored credential. For cross-device approval flows, WWPass's QR-code authentication lets a desktop present a challenge that an admin approves on a bound mobile authenticator, without ever exposing a reusable secret.
See WWPass Passwordless SSO for the architecture overview, WWPass Multi-Factor Authentication for factor options, and the WWPass Developer Documentation for integration specifics your engineering team can act on directly.
FAQ
Do you still need a vault if you're passwordless?
Mostly no, but rarely zero. Human admins should have no passwords, no OTP, no shared secrets, only phishing-resistant login and just-in-time elevation. Machines should get ephemeral credentials at runtime. Keep a shrinking vault only for legacy appliances and out-of-band interfaces that can't yet federate.
How does PAM interact with Zero Trust network segmentation?
They're complementary layers. Segmentation limits blast radius when something goes wrong. PAM reduces the odds and duration of something going wrong in the first place. The policy enforcement point becomes the only front door for privileged protocols, and segmentation rules allow-list the broker's egress rather than every admin's workstation.
What's the difference between passwordless PAM and passkeys for regular users?
Passkeys solve consumer and workforce login. Passwordless PAM applies the same phishing-resistant principle to privileged sessions specifically, and adds just-in-time elevation, session brokering, and command-level control that consumer passkey flows don't cover.
Passwordless privileged access management (PAM) removes passwords and one-time codes from admin logins and replaces them with phishing-resistant authentication, plus just-in-time role activation instead of standing access. It matters because credential theft remains the most common way attackers get into a network, and privileged accounts are the ones worth stealing.
This guide covers what privileged access management is, why passwordless authentication changes its risk profile, the core capabilities a modern PAM program needs, and a rollout plan you can actually execute.
What is privileged access management?
Privileged access management is the set of policies and tools that control how highly empowered identities, human admins, third-party operators, service accounts, and machine identities get, use, and give up elevated rights.
A PAM program governs:
Issuing and recording privileged sessions
Secret vaulting and rotation
Step-up authentication at moments of risk
Approvals and time-bound access
Monitoring and forensic audit trails
NIST and CISA now treat PAM as a core pillar of Zero Trust. Under that model, privileged access is never implicit. It's evaluated per request and verified continuously, not granted once and left standing.
Who counts as a privileged identity?
Privileged identities go well beyond domain admins. They include:
Humans: cloud and infrastructure admins, DBAs, SOC responders, SREs with emergency access, third-party maintainers
Machines: service accounts, workload identities (containers, serverless), CI/CD automation bots, embedded API keys
Non-human identities are often the most dangerous. They tend to be over-provisioned, long-lived, and shared across teams, which makes them attractive to attackers and hard to audit. NIST SP 800-53's AC-2 controls call for formal account management and dynamic activation specifically because unmanaged accounts accumulate into standing privilege, and standing privilege is what turns into an attacker's first foothold.
Why credential theft drives PAM strategy
The 2025 Verizon DBIR found credential abuse is still the most common initial access vector into breached networks, and ransomware was present in 44% of all breaches reviewed, up from 32% the year before.
Every long-lived password, token, or static key is a liability. Every privileged session is a potential launch point for lateral movement. The job of PAM is to shrink that exposure window and require stronger, device-bound proof of identity before granting access.
Why go passwordless for privileged access
Passwordless authentication matters most exactly where the stakes are highest: admin portals, hypervisor consoles, cloud control planes, break-glass entry points, and remote shells.
Phishing is still the dominant way human credentials get stolen. Phishing-resistant multi-factor methods, WebAuthn/FIDO2 or PKI-backed smart cards (PIV/CAC), remove reusable codes entirely and bind the credential to the origin being accessed. That stops credential replay on look-alike sites and closes off push-fatigue and SIM-swap attacks that still work against legacy MFA.
OMB's federal Zero Trust strategy requires agencies to offer phishing-resistant authentication. CISA's guidance narrows that to two accepted patterns: FIDO-based and PKI-based authenticators. For PAM, that means admin sign-in should never depend on a password or a one-time code, especially for high-impact roles.
The problem with vaulted and shared passwords
Traditional PAM vaults reduce password sprawl, but they don't eliminate password risk. Any credential a human can check out can be phished, shoulder-surfed, keylogged, or reused. Pass-the-hash and token replay attacks bypass knowledge of the secret entirely.
A passwordless-first design removes this attack class by refusing to issue passwords to people at all. Humans get origin-bound authenticators; machines get brokered, ephemeral credentials.
Phishing-resistant MFA for admins
WebAuthn binds a private key inside a secure authenticator to a specific origin. The browser won't present that key to a fraudulent site. PKI smart cards achieve the same guarantee through certificate-based mutual TLS or signed assertions.
Both require user presence or verification, pairing something the user has with something the user is. For PAM, require phishing-resistant factors at every role activation or elevation event, not just at initial login.
Ephemeral credentials and just-in-time elevation
Standing privilege is attacker oxygen. PAM should issue rights just-in-time, for a narrow window, and revoke them automatically.
Microsoft Entra PIM is a common example for cloud roles: time- and approval-based activation instead of always-on access. For non-human identities, replace static long-lived credentials with:
Short-duration SSH certificates
Database credentials generated on demand
Cloud role credentials issued via federation instead of stored keys
If a token leaks, it expires fast. If a session goes rogue, revocation is immediate and attributable to a specific event.
Zero Trust principles applied to PAM
Zero Trust places a policy decision point and a policy enforcement point in front of every access request, fed by signals about identity, device, workload, and context.
Applied to PAM, that means privilege elevation isn't a one-time grant. It's conditional and continuously re-evaluated. NIST SP 800-207 sets the pattern: no implicit trust from network location, explicit authorization per resource, continuous monitoring.
Continuous verification and least privilege
Least privilege is a moving target. The right permission at 2:03pm may be wrong at 2:15pm.
Continuous verification uses device posture, geovelocity, workload integrity, and anomaly signals to decide whether a privileged session should continue, be constrained, or be forced to re-authenticate. CISA's Zero Trust Maturity Model v2.0 frames this as a progression from basic login gates to adaptive, risk-informed enforcement.
Policy decision and enforcement points
Model privileged flows with an explicit policy decision point (the policy engine) and policy enforcement point (the broker or connector) in front of every console and protocol.
The enforcement point terminates admin connections, injects credentials, records sessions, enforces command controls, and can cut a session on policy violation. The decision point evaluates identity strength, device health, behavior, resource sensitivity, and ticket linkage before allowing or altering access. This pattern applies whether you're brokering RDP/SSH or approving a cloud role activation.
Segmented admin workstations
Admin activity should originate only from hardened, segmented Privileged Access Workstations (PAWs), never from daily-use endpoints exposed to email and the open web.
Pair PAWs with device-trust checks at the moment of elevation. Don't allow role activation from an unmanaged or non-compliant device, even with perfect credentials.
Core PAM capabilities and where passwordless fits
Capability | What it does | Where passwordless changes it |
|---|---|---|
Credential vaulting and rotation | Stores and rotates secrets for break-glass and legacy systems | Becomes the exception, not the default; short-lived brokered credentials replace human-visible passwords |
Session management | Brokers, records, and controls privileged sessions | Pairs with passwordless admin login and JIT elevation for full forensic coverage |
Approval workflows | Time-boxes access and gates destructive changes | Calibrates friction to risk instead of applying blanket delays |
Secrets management for CI/CD | Issues runtime credentials to apps and pipelines | Short-lived tokens replace embedded static secrets |
Rollout plan
A PAM rollout wins by hardening the systems that would hurt most if abused, not by trying to cover everything at once.
Step 1: Prioritize crown jewels and remote access first.
Front-load two categories: crown-jewel systems (cloud control planes, directory services, hypervisors, CI/CD orchestrators, KMS/HSM consoles, production databases, identity providers, monitoring platforms with write access) and remote access (VPNs, bastion hosts, web admin portals, any management plane exposed to the internet). Commit early to phishing-resistant authentication and just-in-time elevation on both tracks. Defer everything else until those flows are solid.
Step 2: Find the shortcuts.
Prioritization is a living map, not a static spreadsheet. Expect to find shortcut tooling: old consoles kept alive for break/fix, direct RDP/SSH that bypasses the broker, legacy dashboards with super-user cookies. Pull these into scope early so every privileged entry point routes through the same policy engine.
Step 3: Build the admin inventory.
Enumerate every privileged identity and pathway: human roles (cloud, directory, database, SOC, SRE on-call), machines (daemons, scheduled jobs), workloads (containers, serverless), and service accounts. Map each to the consoles, protocols, and APIs they use, and the approvals currently required. Expect to find shadow admins, dormant but dangerous rights inherited through nested groups or old projects.
Step 4: Design the policy model.
Separate "who may ever become privileged" from "who is privileged right now." That's the core of just-in-time access: permissions stay potential until activated by strong authentication, ticket linkage, approval, and context checks.
Step 5: Run a two-stage pilot.
Stage one proves the login ceremony for admin consoles and brokers RDP/SSH sessions through a policy enforcement point that records and enforces policy; confirm device posture checks work and non-compliant endpoints get blocked. Stage two adds approvals and time-boxes, then removes legacy access paths and passwords for the pilot cohort. Exit criteria: no privileged web console accepts passwords or one-time codes for pilot users, all shell access routes through the broker, every elevation requires phishing-resistant step-up and expires, and break-glass is configured and tested.
Step 6: Phase out passwords.
Deprecating passwords is a phased outcome, not a single switch. For each privileged system, track when passwords were last used, by whom, and for what. Where legacy systems force a vault, make sure humans never see the password, use brokered injection or ephemeral certificates, and rotate after every automated use.
Monitoring, audit, and KPIs
A rollout isn't finished until you can prove it works and catch drift before it matters.
What to log: identity, assurance level, and authenticator type; device posture, source IP, and geolocation; policy decisions (allow, deny, step-up required); approvals and justifications; session start/stop, target system, commands, file transfer attempts, and termination reason.
KPIs worth tracking: privileged session count and median duration by system and role; elevation rate and time to approval; emergency access usage and time since last break-glass test; drift between source-of-truth entitlements and actual observed privileges; and password exposure, meaning how many privileged systems still accept passwords or OTP for admins, trending to zero.
Common pitfalls
Leaving recovery flows phishable.
If break-glass or account recovery hinges on email links, SMS codes, or voice calls, an attacker only needs to steer you into that lane to bypass every strong control you built elsewhere. Recovery deserves the same rigor as daily admin login: hardware-backed authenticators, out-of-band checks, minimal exempted accounts, and immediate review after every use.
Shadow admins and unmanaged service accounts.
These accumulate through nested groups, legacy migrations, and one-off exceptions. Run a standing discover-and-remediate loop: flag identities with elevated rights unused in 90 days, accounts without owners, and credentials that never rotate.
Where usernameless and passwordless authentication fits
Origin-bound, hardware-backed authentication is table stakes for privileged accounts. WebAuthn/FIDO2 covers web-based admin consoles. PIV/CAC smart cards remain standard in regulated sectors that require certificate-based authentication.
WWPass takes this further for administrators specifically: usernameless and passwordless sign-in with phishing-resistant authenticators and device binding, built on a distributed zero-trust architecture rather than a single stored credential. For cross-device approval flows, WWPass's QR-code authentication lets a desktop present a challenge that an admin approves on a bound mobile authenticator, without ever exposing a reusable secret.
See WWPass Passwordless SSO for the architecture overview, WWPass Multi-Factor Authentication for factor options, and the WWPass Developer Documentation for integration specifics your engineering team can act on directly.
FAQ
Do you still need a vault if you're passwordless?
Mostly no, but rarely zero. Human admins should have no passwords, no OTP, no shared secrets, only phishing-resistant login and just-in-time elevation. Machines should get ephemeral credentials at runtime. Keep a shrinking vault only for legacy appliances and out-of-band interfaces that can't yet federate.
How does PAM interact with Zero Trust network segmentation?
They're complementary layers. Segmentation limits blast radius when something goes wrong. PAM reduces the odds and duration of something going wrong in the first place. The policy enforcement point becomes the only front door for privileged protocols, and segmentation rules allow-list the broker's egress rather than every admin's workstation.
What's the difference between passwordless PAM and passkeys for regular users?
Passkeys solve consumer and workforce login. Passwordless PAM applies the same phishing-resistant principle to privileged sessions specifically, and adds just-in-time elevation, session brokering, and command-level control that consumer passkey flows don't cover.
Passwordless privileged access management (PAM) removes passwords and one-time codes from admin logins and replaces them with phishing-resistant authentication, plus just-in-time role activation instead of standing access. It matters because credential theft remains the most common way attackers get into a network, and privileged accounts are the ones worth stealing.
This guide covers what privileged access management is, why passwordless authentication changes its risk profile, the core capabilities a modern PAM program needs, and a rollout plan you can actually execute.
What is privileged access management?
Privileged access management is the set of policies and tools that control how highly empowered identities, human admins, third-party operators, service accounts, and machine identities get, use, and give up elevated rights.
A PAM program governs:
Issuing and recording privileged sessions
Secret vaulting and rotation
Step-up authentication at moments of risk
Approvals and time-bound access
Monitoring and forensic audit trails
NIST and CISA now treat PAM as a core pillar of Zero Trust. Under that model, privileged access is never implicit. It's evaluated per request and verified continuously, not granted once and left standing.
Who counts as a privileged identity?
Privileged identities go well beyond domain admins. They include:
Humans: cloud and infrastructure admins, DBAs, SOC responders, SREs with emergency access, third-party maintainers
Machines: service accounts, workload identities (containers, serverless), CI/CD automation bots, embedded API keys
Non-human identities are often the most dangerous. They tend to be over-provisioned, long-lived, and shared across teams, which makes them attractive to attackers and hard to audit. NIST SP 800-53's AC-2 controls call for formal account management and dynamic activation specifically because unmanaged accounts accumulate into standing privilege, and standing privilege is what turns into an attacker's first foothold.
Why credential theft drives PAM strategy
The 2025 Verizon DBIR found credential abuse is still the most common initial access vector into breached networks, and ransomware was present in 44% of all breaches reviewed, up from 32% the year before.
Every long-lived password, token, or static key is a liability. Every privileged session is a potential launch point for lateral movement. The job of PAM is to shrink that exposure window and require stronger, device-bound proof of identity before granting access.
Why go passwordless for privileged access
Passwordless authentication matters most exactly where the stakes are highest: admin portals, hypervisor consoles, cloud control planes, break-glass entry points, and remote shells.
Phishing is still the dominant way human credentials get stolen. Phishing-resistant multi-factor methods, WebAuthn/FIDO2 or PKI-backed smart cards (PIV/CAC), remove reusable codes entirely and bind the credential to the origin being accessed. That stops credential replay on look-alike sites and closes off push-fatigue and SIM-swap attacks that still work against legacy MFA.
OMB's federal Zero Trust strategy requires agencies to offer phishing-resistant authentication. CISA's guidance narrows that to two accepted patterns: FIDO-based and PKI-based authenticators. For PAM, that means admin sign-in should never depend on a password or a one-time code, especially for high-impact roles.
The problem with vaulted and shared passwords
Traditional PAM vaults reduce password sprawl, but they don't eliminate password risk. Any credential a human can check out can be phished, shoulder-surfed, keylogged, or reused. Pass-the-hash and token replay attacks bypass knowledge of the secret entirely.
A passwordless-first design removes this attack class by refusing to issue passwords to people at all. Humans get origin-bound authenticators; machines get brokered, ephemeral credentials.
Phishing-resistant MFA for admins
WebAuthn binds a private key inside a secure authenticator to a specific origin. The browser won't present that key to a fraudulent site. PKI smart cards achieve the same guarantee through certificate-based mutual TLS or signed assertions.
Both require user presence or verification, pairing something the user has with something the user is. For PAM, require phishing-resistant factors at every role activation or elevation event, not just at initial login.
Ephemeral credentials and just-in-time elevation
Standing privilege is attacker oxygen. PAM should issue rights just-in-time, for a narrow window, and revoke them automatically.
Microsoft Entra PIM is a common example for cloud roles: time- and approval-based activation instead of always-on access. For non-human identities, replace static long-lived credentials with:
Short-duration SSH certificates
Database credentials generated on demand
Cloud role credentials issued via federation instead of stored keys
If a token leaks, it expires fast. If a session goes rogue, revocation is immediate and attributable to a specific event.
Zero Trust principles applied to PAM
Zero Trust places a policy decision point and a policy enforcement point in front of every access request, fed by signals about identity, device, workload, and context.
Applied to PAM, that means privilege elevation isn't a one-time grant. It's conditional and continuously re-evaluated. NIST SP 800-207 sets the pattern: no implicit trust from network location, explicit authorization per resource, continuous monitoring.
Continuous verification and least privilege
Least privilege is a moving target. The right permission at 2:03pm may be wrong at 2:15pm.
Continuous verification uses device posture, geovelocity, workload integrity, and anomaly signals to decide whether a privileged session should continue, be constrained, or be forced to re-authenticate. CISA's Zero Trust Maturity Model v2.0 frames this as a progression from basic login gates to adaptive, risk-informed enforcement.
Policy decision and enforcement points
Model privileged flows with an explicit policy decision point (the policy engine) and policy enforcement point (the broker or connector) in front of every console and protocol.
The enforcement point terminates admin connections, injects credentials, records sessions, enforces command controls, and can cut a session on policy violation. The decision point evaluates identity strength, device health, behavior, resource sensitivity, and ticket linkage before allowing or altering access. This pattern applies whether you're brokering RDP/SSH or approving a cloud role activation.
Segmented admin workstations
Admin activity should originate only from hardened, segmented Privileged Access Workstations (PAWs), never from daily-use endpoints exposed to email and the open web.
Pair PAWs with device-trust checks at the moment of elevation. Don't allow role activation from an unmanaged or non-compliant device, even with perfect credentials.
Core PAM capabilities and where passwordless fits
Capability | What it does | Where passwordless changes it |
|---|---|---|
Credential vaulting and rotation | Stores and rotates secrets for break-glass and legacy systems | Becomes the exception, not the default; short-lived brokered credentials replace human-visible passwords |
Session management | Brokers, records, and controls privileged sessions | Pairs with passwordless admin login and JIT elevation for full forensic coverage |
Approval workflows | Time-boxes access and gates destructive changes | Calibrates friction to risk instead of applying blanket delays |
Secrets management for CI/CD | Issues runtime credentials to apps and pipelines | Short-lived tokens replace embedded static secrets |
Rollout plan
A PAM rollout wins by hardening the systems that would hurt most if abused, not by trying to cover everything at once.
Step 1: Prioritize crown jewels and remote access first.
Front-load two categories: crown-jewel systems (cloud control planes, directory services, hypervisors, CI/CD orchestrators, KMS/HSM consoles, production databases, identity providers, monitoring platforms with write access) and remote access (VPNs, bastion hosts, web admin portals, any management plane exposed to the internet). Commit early to phishing-resistant authentication and just-in-time elevation on both tracks. Defer everything else until those flows are solid.
Step 2: Find the shortcuts.
Prioritization is a living map, not a static spreadsheet. Expect to find shortcut tooling: old consoles kept alive for break/fix, direct RDP/SSH that bypasses the broker, legacy dashboards with super-user cookies. Pull these into scope early so every privileged entry point routes through the same policy engine.
Step 3: Build the admin inventory.
Enumerate every privileged identity and pathway: human roles (cloud, directory, database, SOC, SRE on-call), machines (daemons, scheduled jobs), workloads (containers, serverless), and service accounts. Map each to the consoles, protocols, and APIs they use, and the approvals currently required. Expect to find shadow admins, dormant but dangerous rights inherited through nested groups or old projects.
Step 4: Design the policy model.
Separate "who may ever become privileged" from "who is privileged right now." That's the core of just-in-time access: permissions stay potential until activated by strong authentication, ticket linkage, approval, and context checks.
Step 5: Run a two-stage pilot.
Stage one proves the login ceremony for admin consoles and brokers RDP/SSH sessions through a policy enforcement point that records and enforces policy; confirm device posture checks work and non-compliant endpoints get blocked. Stage two adds approvals and time-boxes, then removes legacy access paths and passwords for the pilot cohort. Exit criteria: no privileged web console accepts passwords or one-time codes for pilot users, all shell access routes through the broker, every elevation requires phishing-resistant step-up and expires, and break-glass is configured and tested.
Step 6: Phase out passwords.
Deprecating passwords is a phased outcome, not a single switch. For each privileged system, track when passwords were last used, by whom, and for what. Where legacy systems force a vault, make sure humans never see the password, use brokered injection or ephemeral certificates, and rotate after every automated use.
Monitoring, audit, and KPIs
A rollout isn't finished until you can prove it works and catch drift before it matters.
What to log: identity, assurance level, and authenticator type; device posture, source IP, and geolocation; policy decisions (allow, deny, step-up required); approvals and justifications; session start/stop, target system, commands, file transfer attempts, and termination reason.
KPIs worth tracking: privileged session count and median duration by system and role; elevation rate and time to approval; emergency access usage and time since last break-glass test; drift between source-of-truth entitlements and actual observed privileges; and password exposure, meaning how many privileged systems still accept passwords or OTP for admins, trending to zero.
Common pitfalls
Leaving recovery flows phishable.
If break-glass or account recovery hinges on email links, SMS codes, or voice calls, an attacker only needs to steer you into that lane to bypass every strong control you built elsewhere. Recovery deserves the same rigor as daily admin login: hardware-backed authenticators, out-of-band checks, minimal exempted accounts, and immediate review after every use.
Shadow admins and unmanaged service accounts.
These accumulate through nested groups, legacy migrations, and one-off exceptions. Run a standing discover-and-remediate loop: flag identities with elevated rights unused in 90 days, accounts without owners, and credentials that never rotate.
Where usernameless and passwordless authentication fits
Origin-bound, hardware-backed authentication is table stakes for privileged accounts. WebAuthn/FIDO2 covers web-based admin consoles. PIV/CAC smart cards remain standard in regulated sectors that require certificate-based authentication.
WWPass takes this further for administrators specifically: usernameless and passwordless sign-in with phishing-resistant authenticators and device binding, built on a distributed zero-trust architecture rather than a single stored credential. For cross-device approval flows, WWPass's QR-code authentication lets a desktop present a challenge that an admin approves on a bound mobile authenticator, without ever exposing a reusable secret.
See WWPass Passwordless SSO for the architecture overview, WWPass Multi-Factor Authentication for factor options, and the WWPass Developer Documentation for integration specifics your engineering team can act on directly.
FAQ
Do you still need a vault if you're passwordless?
Mostly no, but rarely zero. Human admins should have no passwords, no OTP, no shared secrets, only phishing-resistant login and just-in-time elevation. Machines should get ephemeral credentials at runtime. Keep a shrinking vault only for legacy appliances and out-of-band interfaces that can't yet federate.
How does PAM interact with Zero Trust network segmentation?
They're complementary layers. Segmentation limits blast radius when something goes wrong. PAM reduces the odds and duration of something going wrong in the first place. The policy enforcement point becomes the only front door for privileged protocols, and segmentation rules allow-list the broker's egress rather than every admin's workstation.
What's the difference between passwordless PAM and passkeys for regular users?
Passkeys solve consumer and workforce login. Passwordless PAM applies the same phishing-resistant principle to privileged sessions specifically, and adds just-in-time elevation, session brokering, and command-level control that consumer passkey flows don't cover.

Get WWPass
Download the WWPass Key app and test authentication without a username or password.
Get WWPass
Download the WWPass Key app and test authentication without a username or password.
