Platform
Solutions
Resources
Company
Platform
Solutions
Resources
Company

Daniel Waldman
∙
Mobile SSO Risks & How WWPass Protects Enterprise Applications
Daniel Waldman
∙
Mobile SSO Risks & How WWPass Protects Enterprise Applications
Daniel Waldman
∙
Mobile SSO Risks & How WWPass Protects Enterprise Applications
Single sign-on (SSO) on a stolen or compromised phone hands an attacker every connected application at once, not just one. That is the core risk this article addresses, and it is why WWPass does not recommend SSO on mobile devices.
The Problem: One Compromised Phone, Every App
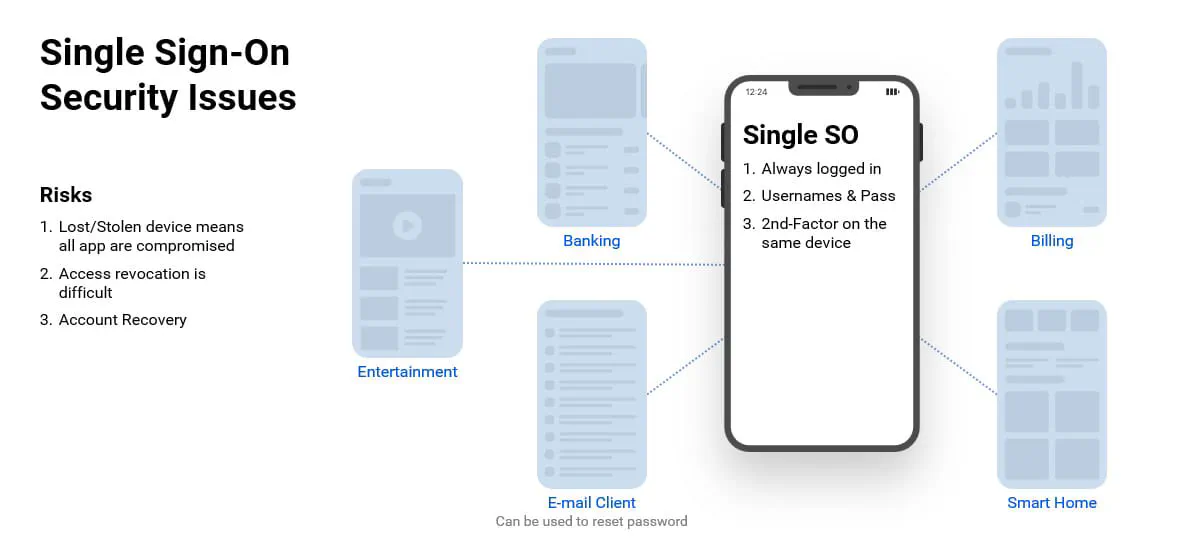
Single sign-on (SSO) has become a popular feature within corporate infrastructures, enabling users to quickly bypass typical security checks to get to applications. It has become common for employees to use SSO along with their personal smartphones to log in to corporate applications. This scenario has major security challenges that, if left unchecked, can spell disaster should someone get hold of an employee's phone.
The top concern anyone should have about their smartphone is whether it's protected should a thief or hacker gain access to it. Unauthorized access can happen if the device is stolen and hacked, or if a hacker gains access by remotely exploiting device software or operating system vulnerabilities. When an SSO system is deployed in the corporate infrastructure, the attacker gets instant access to every ecosystem application used on that device.
Email client applications are a particularly dangerous example. They are commonly left open, with the user always logged in on smartphones. An attacker can not only read sensitive information in email messages, but also use the victim's email account to perform password resets on other accounts. In such cases, SMS or push-based second factors are useless too, because the attacker can receive the verification codes on the compromised device.
How WWPass Multi-Factor Authentication Protects Enterprise Applications
To protect enterprise applications within an SSO ecosystem, it's highly recommended to use multi-factor authentication (MFA) where at least one factor is not already present or accessible on the mobile device. This type of system can actually save time in environments that require frequent re-authentication to applications.
Authentication with the WWPass Key mobile app is more straightforward and less time-consuming than traditional username/password authentication, or authentication that adds a second factor on top of a username and password. With WWPass, there's no need to type usernames, email addresses, or long passwords, all of which waste a user's time. WWPass also doesn't use SMS-based second factors, so users aren't waiting on notifications to arrive.
Instead, WWPass typically only requires users to tap the authentication QR code and enter a PIN or use biometrics (e.g. fingerprint). The whole process is considerably faster than username and password-based authentication, and it's more secure. This lets users authenticate more frequently, for example, authenticating each app separately, while keeping the experience user-friendly. Because authenticating is fast, fewer applications sit in a "logged in" state on the phone at any given time, which reduces what an attacker can reach if the device is stolen or compromised.
PINs Are Never Stored on the Device
WWPass does not verify or store PINs on user smartphones. PIN verification is handled by the WWPass network, which uses the Secure Remote Password (RFC 2945) protocol. SRP guarantees that no PIN-equivalent data is stored on WWPass servers, and the WWPass network has a built-in anti-brute-force mechanism that makes brute-force or wordlist-based attacks on PINs impractical.
If a user's phone falls under an attacker's control, the attacker still needs to guess the PIN to log into an app. With traditional password-based authentication, an attacker can simply reset the password through the user's email. By eliminating email and password logins, WWPass makes that path to unauthorized access far harder to pull off.
Account Recovery Requires More Than Email Access
Unlike traditional authentication solutions that rely solely on email for account recovery, WWPass takes a different approach. To recover access to the WWPass Key app, the user must have access to the email used to back it up and know their PIN, which cannot be reset by email. An attacker is likely to have access to the user's email, but only the user can restore their WWPass Key using their PIN, and the user can permanently block the WWPass Key on a device the attacker controls.
Cryptographic Secrets Stay in Hardware-Backed Storage
WWPass Key stores all cryptographic secrets in hardware-backed cryptographic storage on the user's device (for example, iOS Keychain). In the past, some attacks have extracted keychain information. As of today, according to WWPass, hardware-backed keychains are almost as secure as smartcards.
FAQ
Is SSO safe to use on a mobile device?
WWPass does not recommend using SSO on mobile devices, since a single compromised phone gives an attacker instant access to every connected application at once, rather than just one.
How is WWPass Key authentication faster than a password?
Users tap a QR code and enter a PIN or use biometrics, instead of typing a username, email address, and password. This also reduces how many apps stay logged in on the device at any given time.
Can an attacker reset a WWPass PIN using email access alone?
No. The WWPass PIN cannot be reset by email, and PIN verification is handled by the WWPass network using the SRP (RFC 2945) protocol, so no PIN-equivalent data is ever stored on WWPass servers.
What happens if someone steals a phone with the WWPass Key app on it?
The attacker still needs the PIN to log into any app, and the legitimate user can use their own PIN to recover their WWPass Key and permanently block the key on the attacker's device.

Summary
WWPass does not recommend using single sign-on (SSO) on mobile devices for security reasons.
WWPass offers a straightforward, usernameless and passwordless login experience that provides a higher level of security through more sophisticated multi-factor authentication schemes.
WWPass PIN verification is resistant to brute-force and wordlist-based attacks, and the WWPass PIN cannot be reset via email.
Recovering the WWPass Key app requires the PIN, which protects the key even when an attacker can access the recovery email.
The way WWPass Key stores cryptographic secrets is not vulnerable to the vast majority of attacks.
Single sign-on (SSO) on a stolen or compromised phone hands an attacker every connected application at once, not just one. That is the core risk this article addresses, and it is why WWPass does not recommend SSO on mobile devices.
The Problem: One Compromised Phone, Every App
Single sign-on (SSO) has become a popular feature within corporate infrastructures, enabling users to quickly bypass typical security checks to get to applications. It has become common for employees to use SSO along with their personal smartphones to log in to corporate applications. This scenario has major security challenges that, if left unchecked, can spell disaster should someone get hold of an employee's phone.
The top concern anyone should have about their smartphone is whether it's protected should a thief or hacker gain access to it. Unauthorized access can happen if the device is stolen and hacked, or if a hacker gains access by remotely exploiting device software or operating system vulnerabilities. When an SSO system is deployed in the corporate infrastructure, the attacker gets instant access to every ecosystem application used on that device.
Email client applications are a particularly dangerous example. They are commonly left open, with the user always logged in on smartphones. An attacker can not only read sensitive information in email messages, but also use the victim's email account to perform password resets on other accounts. In such cases, SMS or push-based second factors are useless too, because the attacker can receive the verification codes on the compromised device.
How WWPass Multi-Factor Authentication Protects Enterprise Applications
To protect enterprise applications within an SSO ecosystem, it's highly recommended to use multi-factor authentication (MFA) where at least one factor is not already present or accessible on the mobile device. This type of system can actually save time in environments that require frequent re-authentication to applications.
Authentication with the WWPass Key mobile app is more straightforward and less time-consuming than traditional username/password authentication, or authentication that adds a second factor on top of a username and password. With WWPass, there's no need to type usernames, email addresses, or long passwords, all of which waste a user's time. WWPass also doesn't use SMS-based second factors, so users aren't waiting on notifications to arrive.
Instead, WWPass typically only requires users to tap the authentication QR code and enter a PIN or use biometrics (e.g. fingerprint). The whole process is considerably faster than username and password-based authentication, and it's more secure. This lets users authenticate more frequently, for example, authenticating each app separately, while keeping the experience user-friendly. Because authenticating is fast, fewer applications sit in a "logged in" state on the phone at any given time, which reduces what an attacker can reach if the device is stolen or compromised.
PINs Are Never Stored on the Device
WWPass does not verify or store PINs on user smartphones. PIN verification is handled by the WWPass network, which uses the Secure Remote Password (RFC 2945) protocol. SRP guarantees that no PIN-equivalent data is stored on WWPass servers, and the WWPass network has a built-in anti-brute-force mechanism that makes brute-force or wordlist-based attacks on PINs impractical.
If a user's phone falls under an attacker's control, the attacker still needs to guess the PIN to log into an app. With traditional password-based authentication, an attacker can simply reset the password through the user's email. By eliminating email and password logins, WWPass makes that path to unauthorized access far harder to pull off.
Account Recovery Requires More Than Email Access
Unlike traditional authentication solutions that rely solely on email for account recovery, WWPass takes a different approach. To recover access to the WWPass Key app, the user must have access to the email used to back it up and know their PIN, which cannot be reset by email. An attacker is likely to have access to the user's email, but only the user can restore their WWPass Key using their PIN, and the user can permanently block the WWPass Key on a device the attacker controls.
Cryptographic Secrets Stay in Hardware-Backed Storage
WWPass Key stores all cryptographic secrets in hardware-backed cryptographic storage on the user's device (for example, iOS Keychain). In the past, some attacks have extracted keychain information. As of today, according to WWPass, hardware-backed keychains are almost as secure as smartcards.
FAQ
Is SSO safe to use on a mobile device?
WWPass does not recommend using SSO on mobile devices, since a single compromised phone gives an attacker instant access to every connected application at once, rather than just one.
How is WWPass Key authentication faster than a password?
Users tap a QR code and enter a PIN or use biometrics, instead of typing a username, email address, and password. This also reduces how many apps stay logged in on the device at any given time.
Can an attacker reset a WWPass PIN using email access alone?
No. The WWPass PIN cannot be reset by email, and PIN verification is handled by the WWPass network using the SRP (RFC 2945) protocol, so no PIN-equivalent data is ever stored on WWPass servers.
What happens if someone steals a phone with the WWPass Key app on it?
The attacker still needs the PIN to log into any app, and the legitimate user can use their own PIN to recover their WWPass Key and permanently block the key on the attacker's device.
Summary
WWPass does not recommend using single sign-on (SSO) on mobile devices for security reasons.
WWPass offers a straightforward, usernameless and passwordless login experience that provides a higher level of security through more sophisticated multi-factor authentication schemes.
WWPass PIN verification is resistant to brute-force and wordlist-based attacks, and the WWPass PIN cannot be reset via email.
Recovering the WWPass Key app requires the PIN, which protects the key even when an attacker can access the recovery email.
The way WWPass Key stores cryptographic secrets is not vulnerable to the vast majority of attacks.

Get WWPass
Download the WWPass Key app and test authentication without a username or password.
Get WWPass
Download the WWPass Key app and test authentication without a username or password.
